

Before offering an answer to this question circulating lately in the world of cybersecurity, we must have an idea of where this question comes from and of what SIEM and SOAR can offer the SOC and the management of threats and vulnerabilities.
SIEM, the window of the SOC
SIEM or Security Information and Event Management is an essential tool within every security center. This tool allows security teams to read, understand and interpret the countless logs received from all the IS equipment: firewall logs, workstations, applications, etc…
SIEM also enables the creation of scenarios and alerts based on the correlation of data received from the company’s different devices.
To explain a bit more what a SIEM can offer, we will look at a use case that can be found in any company.
Suppose a malicious email has found its way to a user’s mailbox, and that user, unfortunately, clicked on the link or attachment contained in the email, which caused a whole procedure of contamination of the workstation and the network to be triggered.
By collecting the logs of the mail servers, network nodes, workstations and Active Directory, we can see that the attacker tries to contact an external server (workstation log); after downloading, the malware tries to create a user account on Active Directory (AD log); using this account and the victim’s account, the user tries to gain access to other workstations using known flaws (workstation log).
Using all of these logs and all of this information, the SIEM will create a sort of attack path or chain, following the traces, dates and actions ; the security teams in the SOC will quickly and easily know the first point of entry and the impacted services so they can remediate and stop the infection and the attack in progress.
However, despite all its successes, SIEM has several weaknesses, including the difficulty and complexity of scalability but also the number of false positives that require an enormous amount of processing time, knowing that logs never stop and that detection in a SOC is done 24 hours a day, 7 days a week and 365 days a year. Also, it requires a very well-trained team to be able to manage all this.
SOAR, a major asset for the SOC in terms of time savings
As a set of software and tools, SOAR (Security Orchestration, Automation and Response) makes it possible to detect and act on low-level incidents but also to add layers of management of possible vulnerabilities and threats. It also makes it possible to orchestrate and automate these tasks to save time. Thus, in addition to alerting the CSIRT in particular, SOAR will automatically add blocking rules at the firewall level and create incident tickets that it will send to the teams concerned.
If we take the SOC example again, SOAR will even be able to disconnect the workstation that opened the attachment, temporarily block the AD account created by the attacker and send alerts to all parties concerned. With good configuration and adaptation, SOAR will minimize damage and save precious time for the SOC engineers.
This is what explains why several security experts think that SOAR answers the questions that SIEM leaves unanswered.
And why not a complementarity between the two?
In the most advanced SOCs, SOAR and SIEM are observed working in perfect complementarity, although several opinions lean toward SOAR entirely replacing SIEM.
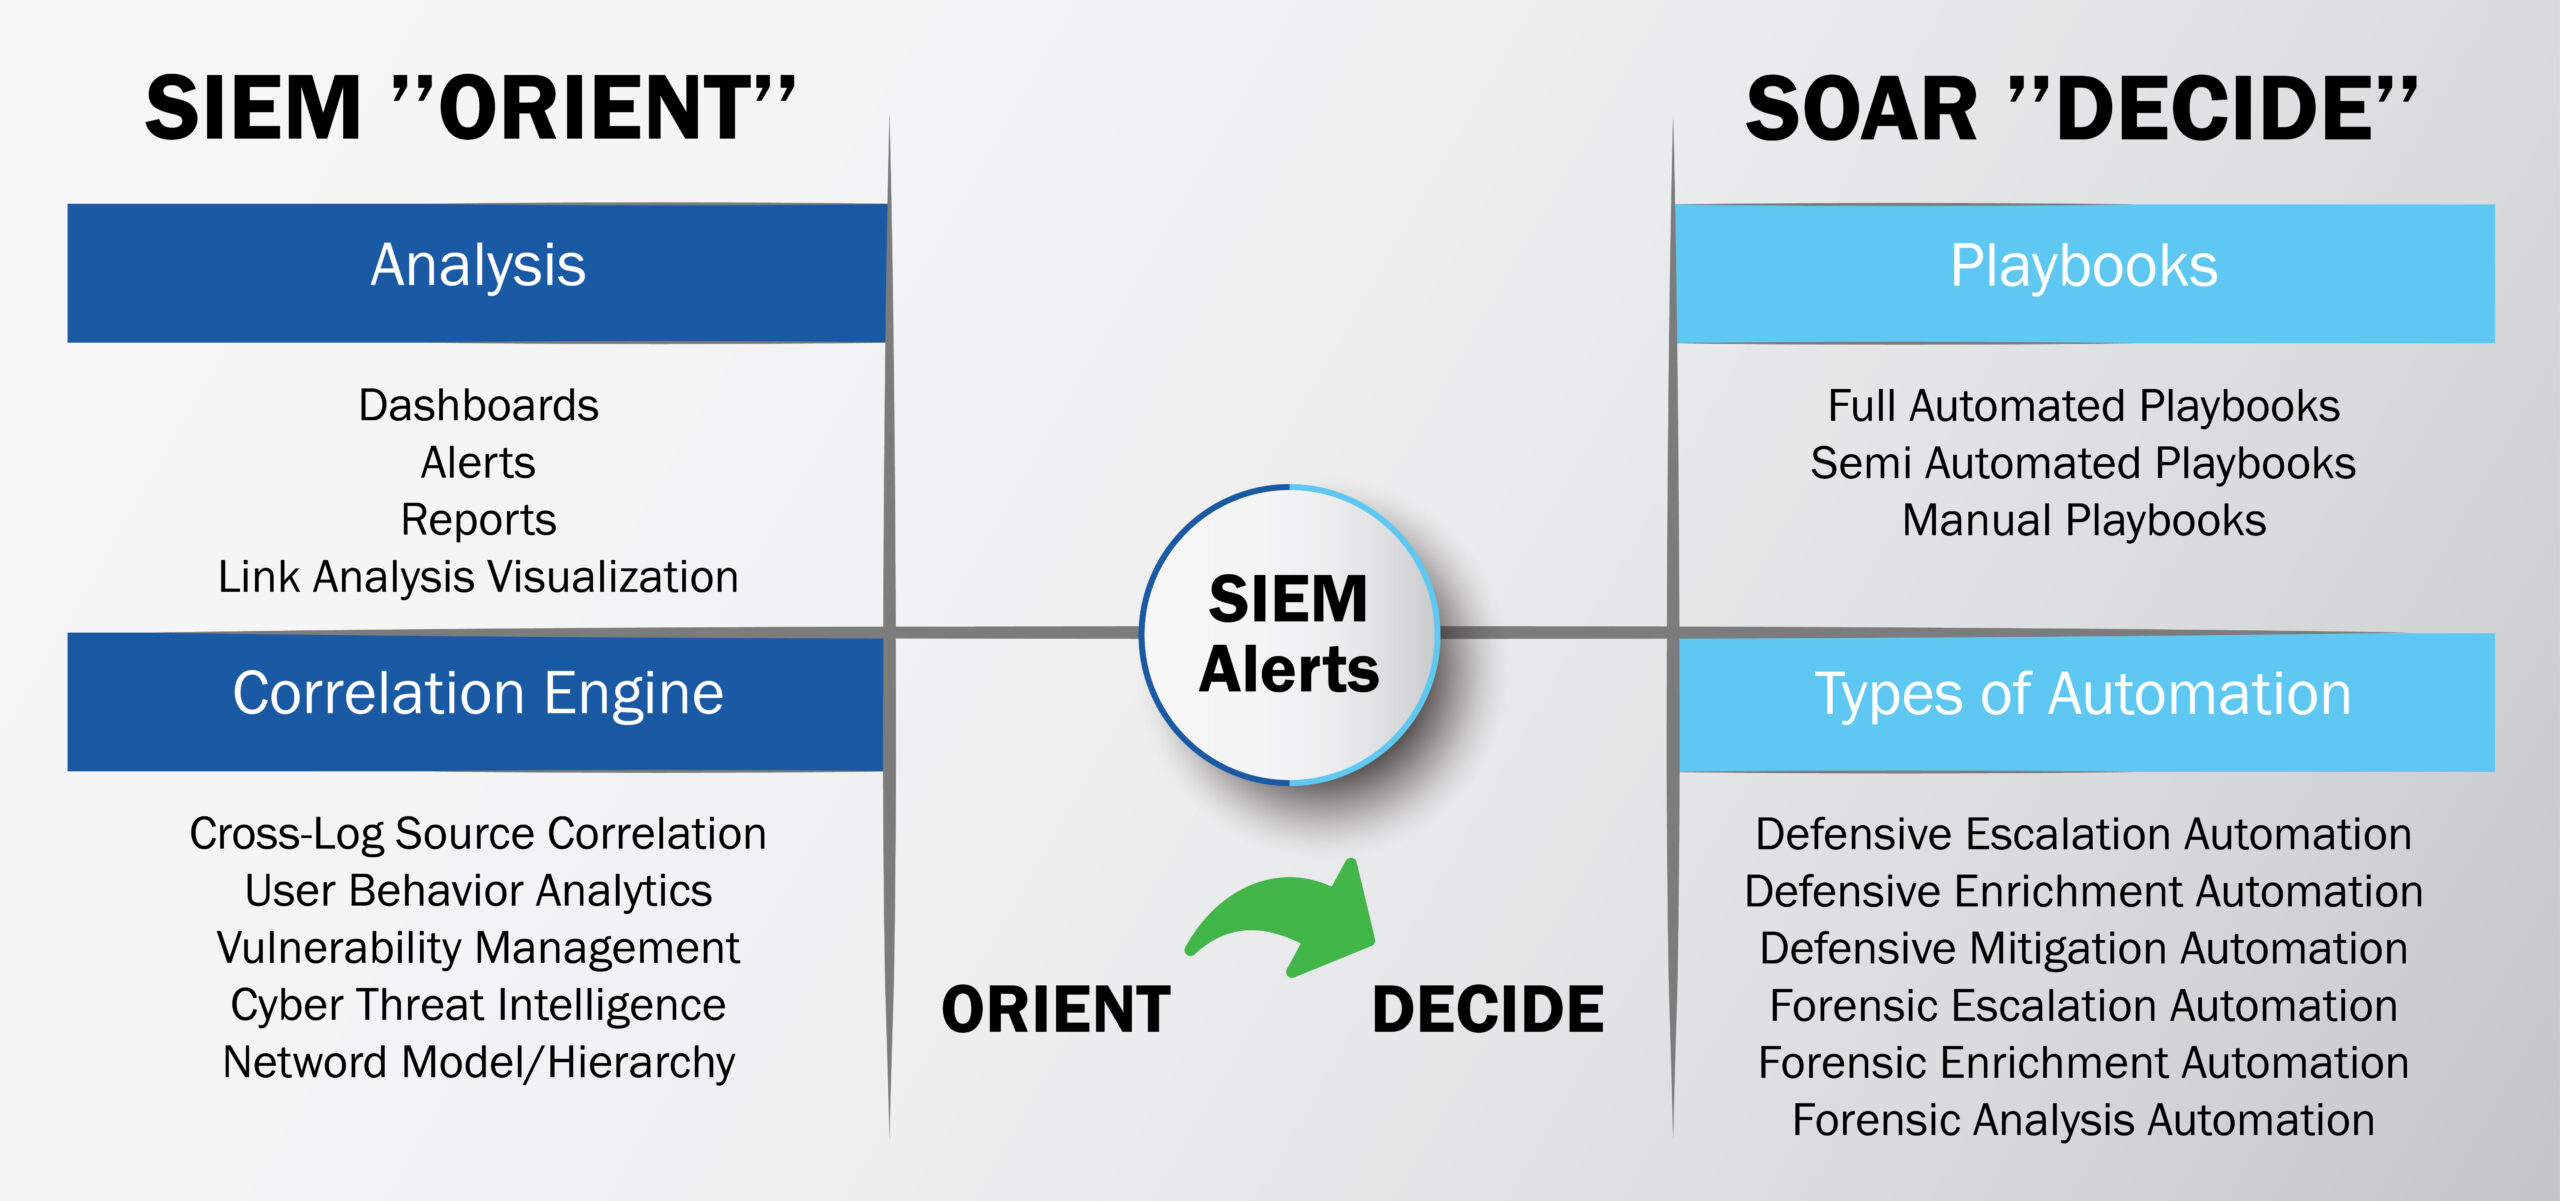
We nevertheless note that SIEMs improve over time and add next-gen features to better help security experts manage the challenges of cybersecurity.
After several comparisons, we believe that SIEM will not be replaced by SOAR but on the contrary, like any good product, SIEM will be open to cooperation with SOAR for the creation of a complete solution ready to face the challenges of the future. The mix between the two can increase the SOC’s effectiveness.


